


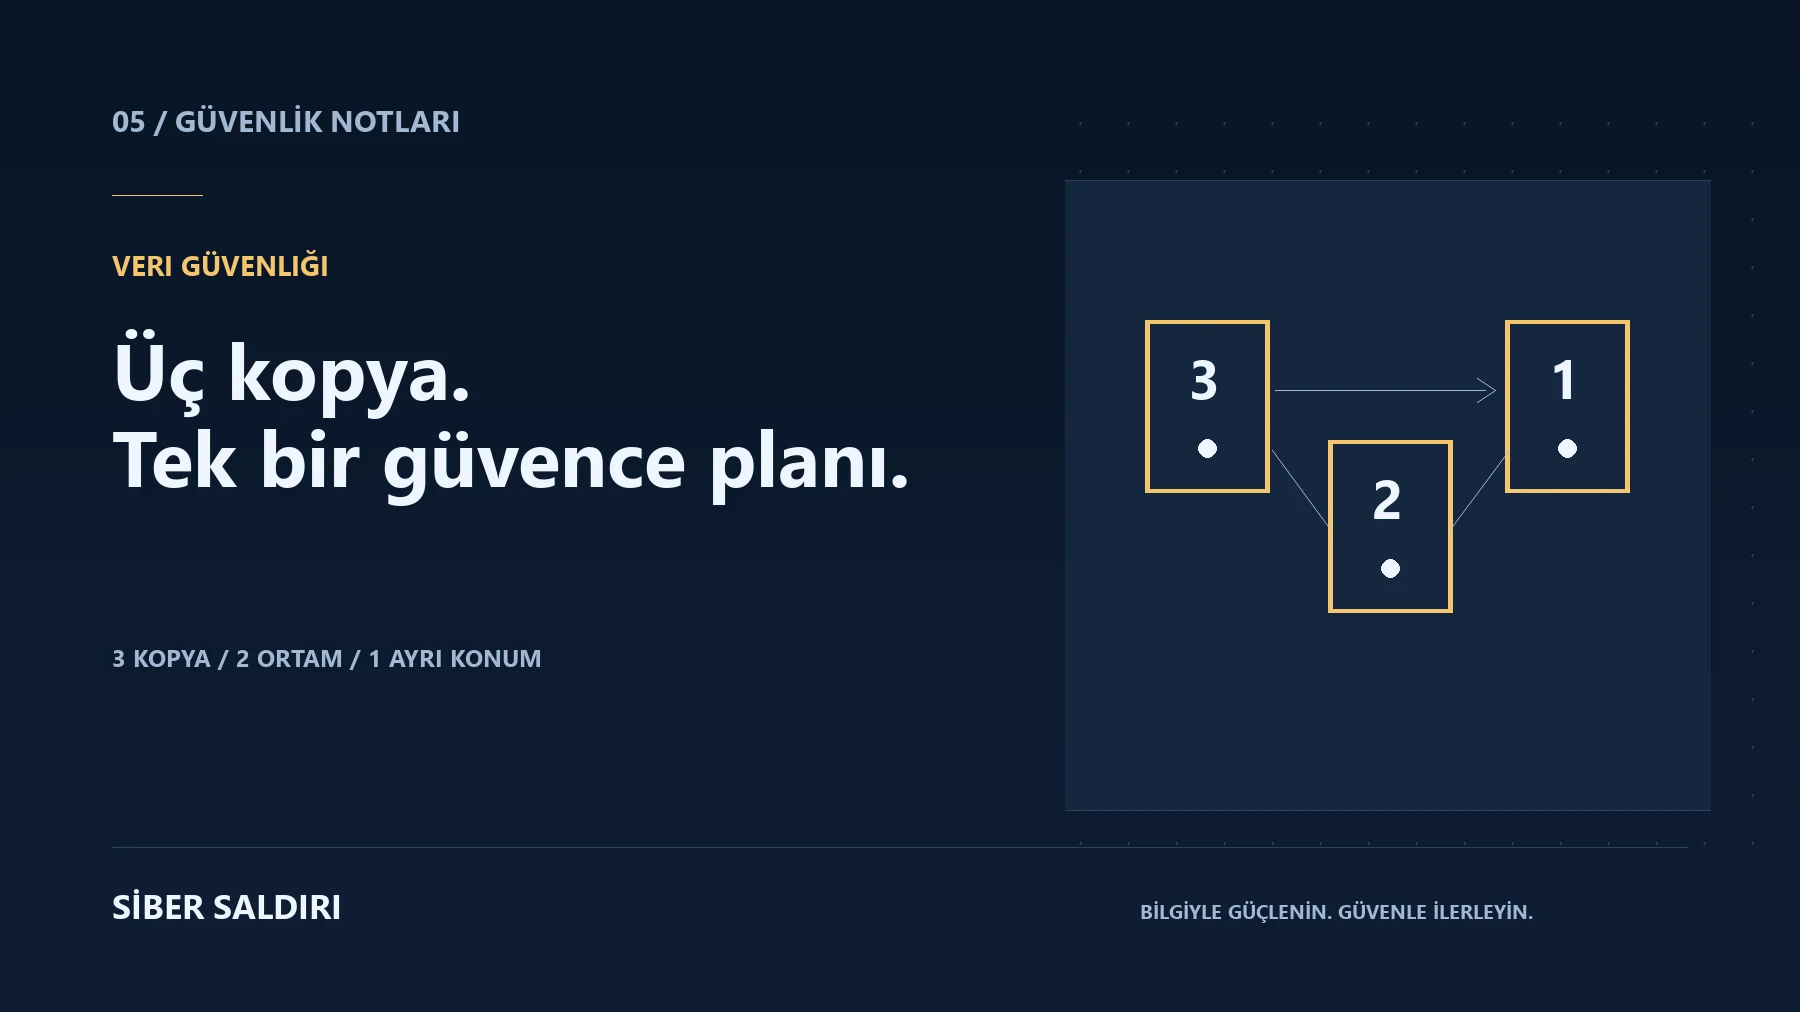
The 3-2-1 backup approach aims to keep a total of three copies of data, distributing them across two different media or independent fault sites, and storing one copy in a separate location. The goal is to make it difficult for a single failure or event to affect all replicas at the same time. Access security and restorability are as important as the existence of copies.
Difference between sync and backup
Syncing keeps files up to date across devices. Accidental deletion or corruption of a file may be reflected on other devices. Backup aims to return data at a certain point in time. A service can offer both features; The important thing is that you really know the version retention period, retention of deleted data, and restore options.
Sample backup plan for home user
Working files can be kept on the computer, a regular backup on an external disk, and a second protected copy on storage in a separate location. If the external disk is left connected constantly, it may be affected by the same malware or electrical malfunction. Secure separation after copying provides additional protection in appropriate usage scenarios.
This example is not the only correct setup. Large files, internet quota and number of devices affect your choice. The important thing is to know in advance where, to what date and how long you can get back to when a file is deleted.
What should businesses measure?
RPO, acceptable data loss range; RTOrefers to the targeted time for the service to return. A business that takes daily backups may lose its work since the last backup, depending on the circumstances. It does not take the same amount of time for a file to be returned and for the entire accounting system to be operational.
- Clearly list which data and application are being backed up.
- Separate backup accounts from daily administrative accounts.
- Separately protect encryption keys and recovery information.
- Verify the configuration of offline or immutable replicas.
- Have a responsible person monitor backup failures.
How to do restore testing?
- Start with non-critical sample files and record the testing date.
- Restore the file to a separate location without overwriting live data.
- Check that the file opens and contains the expected content.
- Verify that the authorized person has access to the required passwords or keys.
- Test that the database and dependencies return together in application backups.
- Compare the actual time to your target recovery time.
Just because a backup job appears “successful” does not necessarily prove that the files are usable. Regular restore attempts can uncover missing folders, forgotten keys, and too short retention periods without incident.
Frequently asked questions
Can two copies be in different folders on the same disk?
This does not provide independent protection against disk failure. It is necessary to distribute the copies into separate error areas.
How often should backup be done?
It is determined by the data loss you can accept. Business data that changes frequently during the day and an archive that is updated monthly may not require the same plan.
Continue: protection from ransomware and backup guide.
Source and further reading
CISA: How to Protect the Data that is Stored on Your Devices. Source check date: 17 October 2026.
